
Official Security Advisory and Remediation Guidance for Topsee NVR Devices (CVE-2026-100886)
- Vulnerability
- CVE-2026-100886 — Unauthenticated access to the debug service (CVSS 10.0, Critical)
- Status
- Fixed — patch released
- Official fix version
- NVR firmware 4.6.2.0 (TS81xxD3x, TS8232C10 and TS8xxxG series) — released October 29, 2026
- Affected models
- T8108, T8108P, T8116, T8232
- Affected firmware
- 4.6.1.4-build202604241011 and similar earlier versions
- Security contact
- security@tpsee.com
Official Vendor Response Statement
To all Topsee users and partners:
Topsee has confirmed a security vulnerability affecting certain NVR models, tracked as CVE-2026-100886 and disclosed by third-party security platforms. We treat this matter with the highest priority. Upon receiving the report we immediately activated our top-level incident response process, and our engineering team has completed a permanent fix.
The fix is now available. NVR firmware version 4.6.2.0 was released on October 29, 2026 and fully resolves this issue. It is available for download from the Topsee official website; connected devices will also receive an upgrade prompt automatically, and the upgrade notice is pushed through the device management interface and the Seetong APP.
Until the upgrade is completed, please keep the device protected: if the device is not exposed to the public internet (LAN-only use), it is not at risk. If it is exposed, follow the urgent guidance in the FAQ section below and place the device behind a firewall. For any questions, contact us at security@tpsee.com.
Frequently Asked Questions about CVE-2026-100886
A: The vulnerability lies in the device debug service component. It is rated CVSS 10.0 (Critical) and is an unauthenticated access issue — an attacker needs no username or password to reach the debug service. If the device is directly exposed to the public internet, the risk is extremely high. If it is not exposed and used only on a local network, external attackers cannot reach it. The issue is fixed in firmware 4.6.2.0, released October 29, 2026.
A: Check the model and firmware version of the device:
- Affected models: T8108, T8108P, T8116, T8232
- Affected firmware: 4.6.1.4-build202604241011 and similar earlier versions
* Models not on this list are at lower risk. We still recommend following safe networking practices and keeping firmware up to date.
A: As long as the device is used on a local network with no public port forwarding, external attackers cannot exploit this vulnerability. However, the fix is already available, so upgrading to firmware 4.6.2.0 is still recommended. Reviewing firewall settings is also advised for absolute safety.
A: Please take the following steps immediately:
- Upgrade the firmware to 4.6.2.0 or later — this fully fixes the vulnerability.
- Remove port forwarding: log in to the router or firewall and delete any port-forwarding rules created for this NVR (especially TCP port 3000). Put the device behind a firewall.
- Network isolation: place the device in a dedicated, isolated VLAN.
- Block external access: on the perimeter firewall, explicitly deny all inbound access from external networks to the device debug port (TCP 3000).
* If network configuration is unfamiliar, contact the installer of the device or internal IT staff for assistance immediately.
A: Yes. NVR firmware 4.6.2.0 was released on October 29, 2026 and is available now. It fully resolves this issue. Two ways to upgrade:
- Automatic: keep the device connected to the network — it will prompt you to upgrade automatically, and the notice is also pushed through the Seetong APP.
- Manual: download firmware 4.6.2.0 from the "Download — Firmware upgrade Download — NVR" section of the Topsee official website and upgrade manually.
* White-label / OEM customers: contact the device supplier to obtain the 4.6.2.0 upgrade package.
A: The vulnerability is fully fixed after upgrading to 4.6.2.0. However, as a security best practice, we never recommend exposing any surveillance device (NVR or IPC) directly to the public internet. For remote viewing, use the official P2P feature of the Seetong APP, or connect through an encrypted VPN tunnel. Never expose management ports directly.
A: Yes. This firmware is also shipped under certain downstream brands. If an OEM NVR based on this platform is in use, follow the same guidance, upgrade to 4.6.2.0, and contact the device supplier to obtain the upgrade package.
Q8. Has the vendor responded to this disclosure?
A:Yes. Topsee has formally responded. This page is the official vendor statement issued by Shenzhen Topsee Technology Co., Ltd. The confirmed fix is NVR firmware version 4.6.2.0 for the TS81xxD3x, TS8232C10 and TS8xxxG series, released on October 29, 2026 and now available. Interim mitigation measures are published above for users who have not yet upgraded. Further updates will be posted on this page.
Official security contact
Email: security@tpsee.com (vulnerability reports and remediation inquiries)
Firmware download: visit the "Download — Firmware upgrade Download — NVR" section of the Topsee official website for NVR 4.6.2.0
This advisory is issued by Shenzhen Topsee Technology Co., Ltd. Any further updates will be posted on this page without separate notice.
-
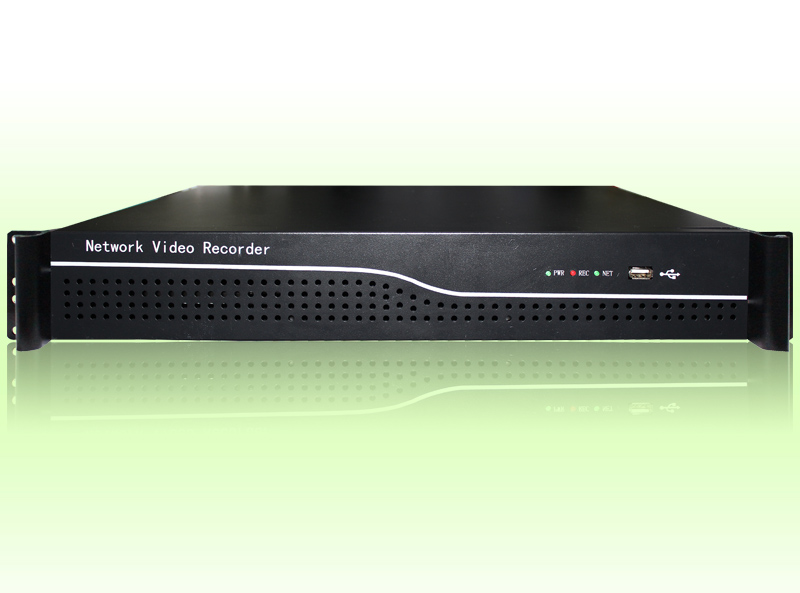 TS8864G 64-ch 2U 4K H265+ NVR
Nvr4.0 H.265 series 64 channel network video recorder
-
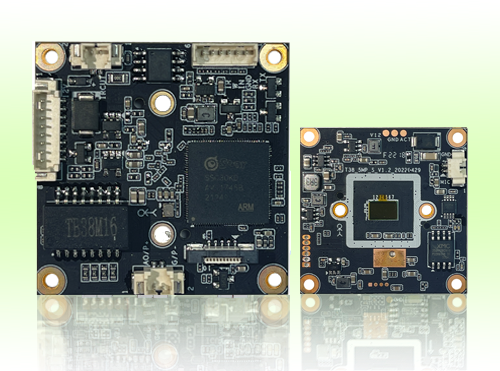 5 MP 38*38mm black light
TB38M16
-
.png) 2 MP 53*53mm black light WIFI TF card
TD53J20
-
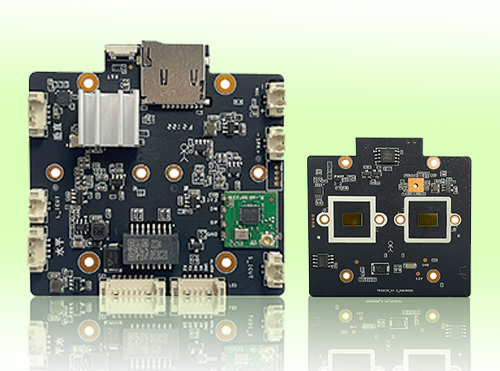 4 MP 53*53mm black light binocular WIFI TF card
TD53C20
-
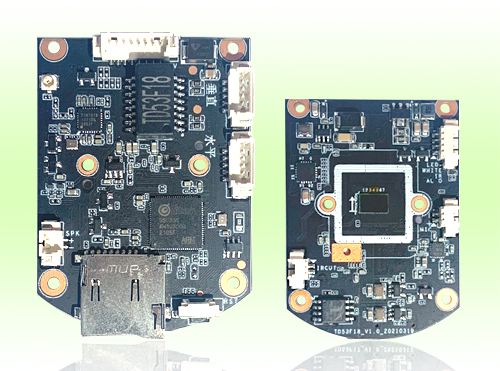 3 MP 53*53mm dual light WIFI TF card
TD53F18
-
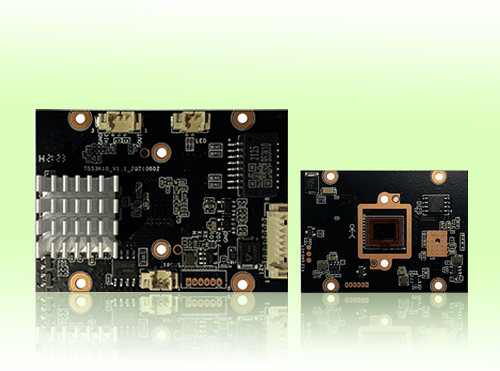 8 MP 42*42mm black light
TB53K20
-
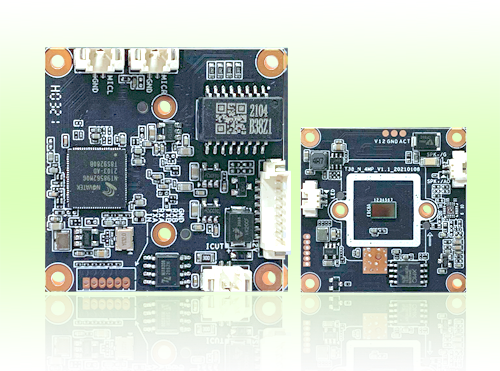 4 MP 38*38mm black light
TB38Z20
-
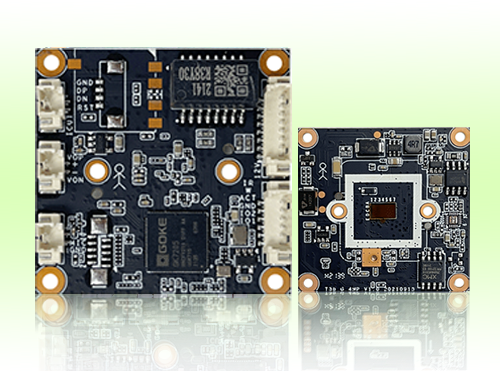 4 MP 38*38mm dual light
TR38Y30